

GDPR Is Coming Soon … and Companies Aren’t Ready
GDPR Is Coming Soon … and Companies Aren’t Ready
The E.U. General Data Protection Regulation will impact all companies that have customers in Europe, but many organizations haven’t started preparing for it.
Awareness Exists
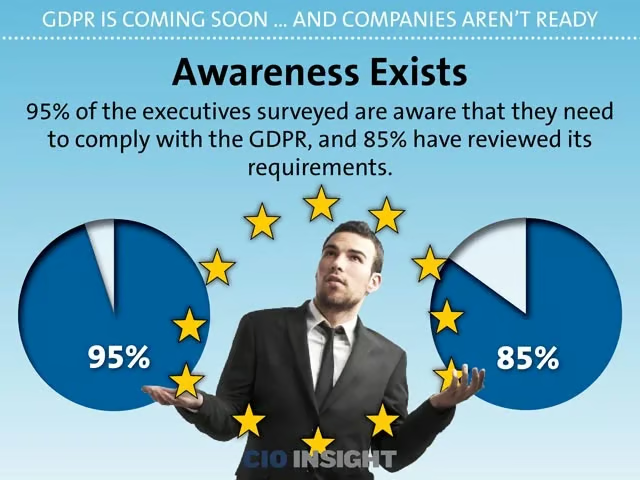
95% of the executives surveyed are aware that they need to comply with the GDPR, and 85% have reviewed its requirements.
Feeling Secure
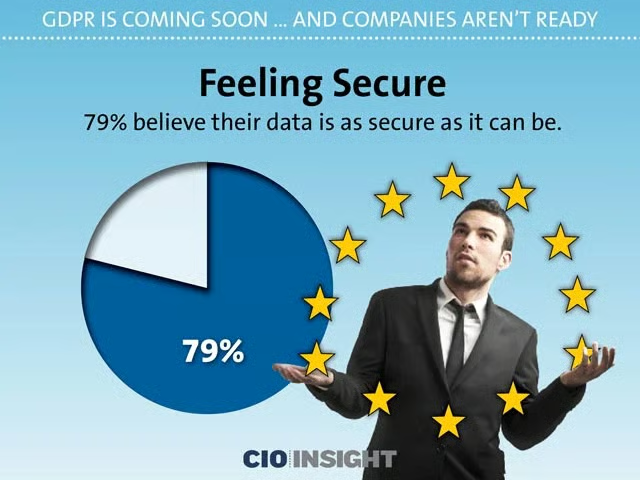
79% believe their data is as secure as it can be.
False Sense of Security?
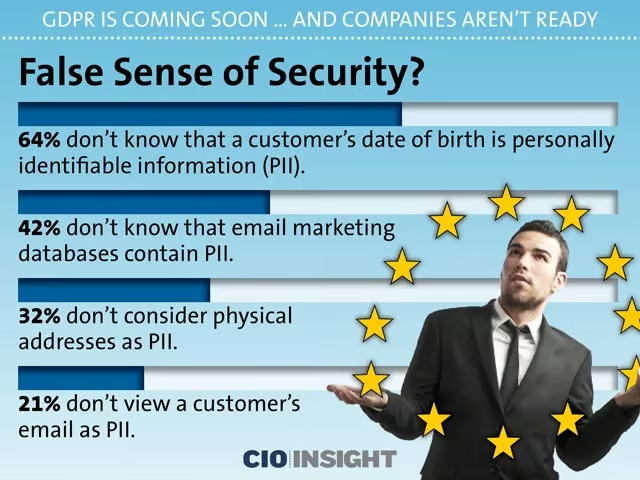
64% don’t know that a customer’s date of birth is personally identifiable information (PII).
42% don’t know that email marketing databases contain PII.
32% don’t consider physical addresses as PII.
21% don’t view a customer’s email as PII.
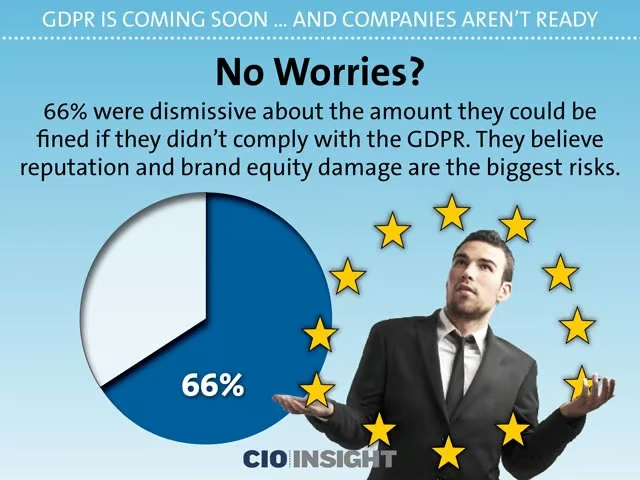
No Worries?
66% were dismissive about the amount they could be fined if they didn’t comply with the GDPR. They believe reputation and brand equity damage are the biggest risks.
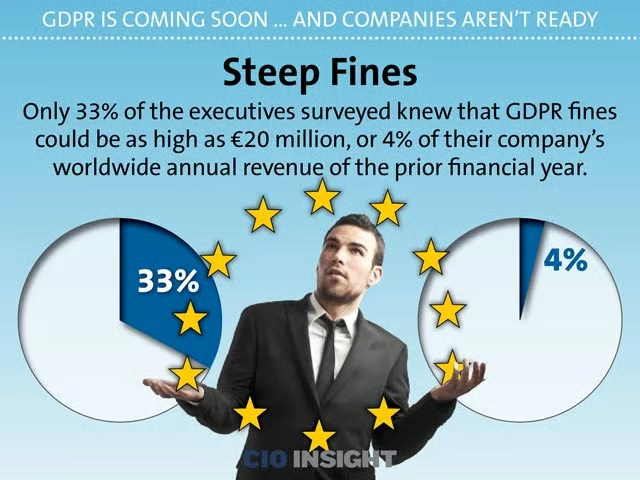
Steep Fines
Only 33% of the executives surveyed knew that GDPR fines could be as high as €20 million, or 4% of their company’s worldwide annual revenue of the prior financial year.
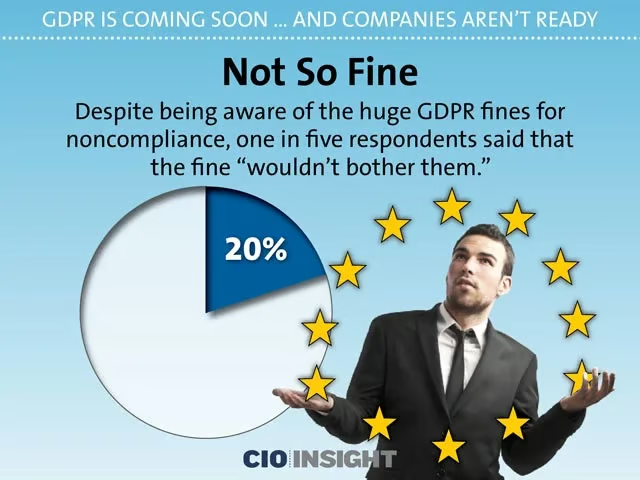
Not So Fine
Despite being aware of the huge GDPR fines for noncompliance, one in five respondents said that the fine “wouldn’t bother them.”
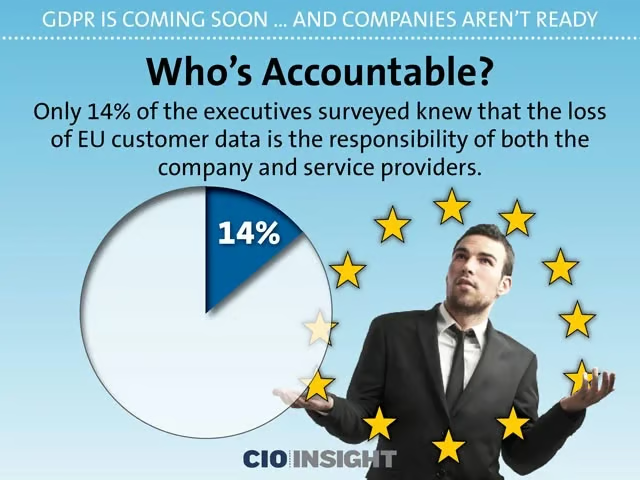
Who’s Accountable?
Only 14% of the executives surveyed knew that the loss of EU customer data is the responsibility of both the company and service providers.
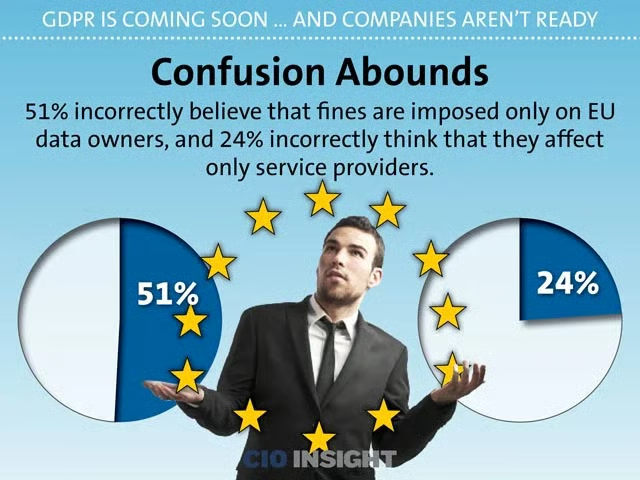
Confusion Abounds
51% incorrectly believe that fines are imposed only on EU data owners, and 24% incorrectly think that they affect only service providers.
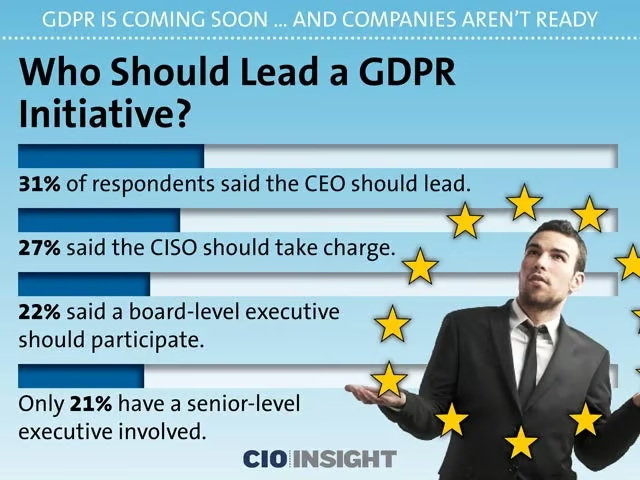
Who Should Lead a GDPR Initiative?
31% of respondents said the CEO should lead, and 27% said the CISO should take charge. 22% said a board-level executive should participate. Yet, only 21% have a senior-level executive involved.
Mandate: State-of-the-Art Tech
The GDPR mandates that businesses must implement state-of-the-art security technologies that are relative to the risks faced.
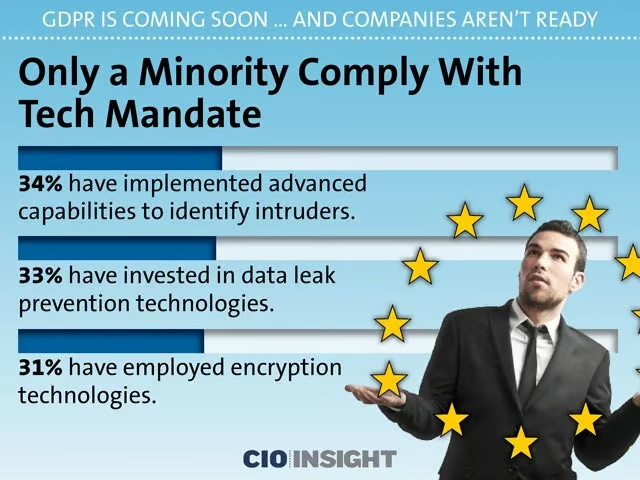
Only a Minority Comply With Tech Mandate
34% have implemented advanced capabilities to identify intruders.
33% have invested in data leak prevention technologies.
31% have employed encryption technologies.